

Event Tracing for Windows (ETW) is an efficient kernel-level tracing facility that lets you log kernel or application-defined events to a log file. You can consume the events in real-time or from a log file and use them to debug an application or to determine where performance issues are occurring in the application. ETW lets you enable or disable event tracing dynamically, allowing you to perform detailed tracing in a production environment without requiring computer or application restarts. Here are some related guides: how to work with Windows Performance Toolkit, and What is ADK, MDT, Microsoft Endpoint Configuration Manager (SCCM), Intune, Autopilot, and WSUS.
The Event Tracing for Windows (ETW) infrastructure provides the foundation for Windows Performance Toolkit. These tools provide a set of programs that hide the complexity of working directly with the ETW application programming interfaces (APIs). ETW is included in Microsoft Windows 2000 and later.
You can use the .NET TraceProcessing API to analyze ETW traces for your applications and other software components. This API is available as a NuGet package. The Event Tracing API is broken into three distinct components:
- Controllers, which start and stop an event tracing session and enable providers
- Providers, which provide the events
- Consumers, which consume the events
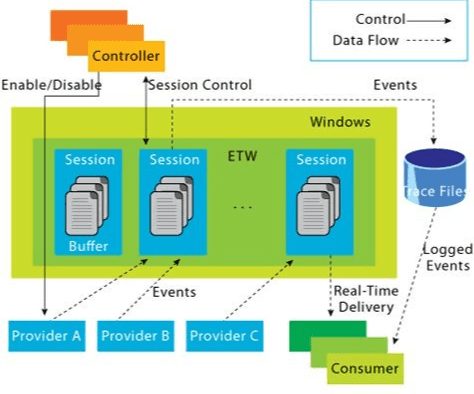
The following diagram shows the event tracing model. Also, we will be discussing the various components extensively. Wish to improve your Debugging And Performance Tuning With ETW.
Controllers
Controllers are applications that define the size and location of the log file, start and stop event tracing sessions, enable providers so they can log events to the session, manage the size of the buffer pool, and obtain execution statistics for sessions.
Session statistics include the number of buffers used, the number of buffers delivered, and the number of events and buffers lost.
Providers
Providers are applications that contain event tracing instrumentation. After a provider registers itself, a controller can then enable or disable event tracing in the provider. The provider defines its interpretation of being enabled or disabled.
Generally, an enabled provider generates events, and a disabled provider does not. This lets you add event tracing to your application without requiring that it generate events all the time.
Although the ETW model separates the controller and provider into separate applications, an application can include both components. There are four main types of providers:
- MOF (classic) providers,
- WPP providers,
- manifest-based providers, and
- TraceLogging providers.
Note: You should use a manifest-based provider or a TraceLogging provider if you are writing applications for Windows Vista or later that do not need to support legacy system
Consumers
Consumers are applications that select one or more event tracing sessions as a source of events. A consumer can request events from multiple event tracing sessions simultaneously; the system delivers the events in chronological order.
Consumers can receive events stored in log files, or from sessions that deliver events in real-time. When processing events, a consumer can specify start and end times, and only events that occur in the specified time frame will be delivered.
More information on Event Tracing for Windows (ETW)
ETW enables the consistent, straightforward capture of kernel and application events. Enabling or disabling event capture at any time doesn’t require a system or process restart. Windows Performance Analyzer (WPA) presents the information that ETW collects in an easy-to-understand set of graphs and tables.
You can capture and present selected events to non-invasively identify and diagnose system and application performance issues. You can enable or disable event tracing dynamically. Windows Performance Recorder (WPR) uses ETW to gather and organize critical system information. WPR acts as the session controller, starting and stopping the session and selecting which ETW events to record.
WPA consumes the event trace log (ETL) file that all event providers produce in an ETW session. Kernel and application events can provide extensive details about the operation of the system. Almost every kernel event that affects overall system performance is defined and available to WPA.
Why do we have to perform Event Tracing?
Event Tracing for Windows (ETW) provides application programmers the ability to start and stop event tracing sessions, instrument an application to provide trace events, and consume trace events.
Trace events contain an event header and provider-defined data that describes the current state of an application or operation. You can use the events to debug an application and perform capacity and performance analysis.
When, and where to use Event Tracing?
Use ETW when you want to instrument your application, log user or kernel events to a log file, and consume events from a log file or in real-time.
I hope you found this blog post on event tracing for windows helpful. If you have any questions do not hesitate to ask in the comment section.


