In this article, we shall discuss how to Perform BitLocker Recovery Password Rotation in Active Directory. Kindly see, How to Change BitLocker Password in Windows and how to Force BitLocker Recovery mode: How to unlock BitLocker Protected Drive. Maintaining the security of BitLocker-encrypted drives is crucial. Situations may arise where users forget their PINs or significant changes in the system configuration necessitate the use of the 48-character BitLocker recovery key.
Often, users are not at their desks and may need the key communicated via phone or mobile device, which presents a security risk. Users might write down the recovery password or store it insecurely. Therefore, it’s best for users not to know the recovery key. If they must use it, then the key should be renew immediately afterward.
Here are other related guides: Manage BitLocker and FileVault with Trellix Native Encryption, Install BitLocker on Windows Server via the Server Manager, and How to Prevent Standard Users from Changing BitLocker Password.
Creating a New Key Protector
Tools like manage-bde and PowerShell are essential for managing BitLocker keys. While they don’t directly update the recovery password, you can remove the old one and generate a new one. In PowerShell, you will use Add-BitLockerKeyProtector and Remove-BitLockerKeyProtector cmdlets for this purpose.
Below is a script designed to renew the recovery password for the system drive ($env:SystemDrive). You can modify the MountPoint parameter as necessary. The -WarningAction SilentlyContinue parameter ensures that the new key is not displayed on the console.
Open PowerShell as administrator and run the script below:

# Generate a new RecoveryPassword protector$newRecoveryKey = Add-BitLockerKeyProtector -MountPoint $env:SystemDrive -RecoveryPasswordProtector -WarningAction SilentlyContinue

If Add-BitLockerKeyProtector is executed without -WarningAction, the new key will be displayed on the screen as shown below:
# Generate a new RecoveryPassword protector$newRecoveryKey = Add-BitLockerKeyProtector -MountPoint $env:SystemDrive -RecoveryPasswordProtector

The above script stores the old BitLocker recovery passwords each time you run it. To verify this, enter the cmdlet below:
manage-bde -protectors -get C:

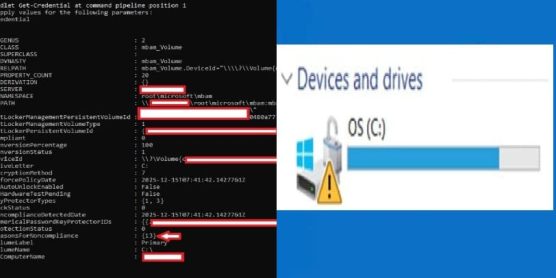
Please see How does Key Rotation work in MBAM? Also, see “Manage TPM Protector: How to encrypt additional drives on an MBAM-protected device“, and “How to determine why an MBAM-protected device is non-compliant.
Removing Old Recovery Passwords from Active Directory
When a new recovery key is created and stored in AD using a Group Policy Object (GPO), the old key becomes obsolete but remains in the msFVE-RecoveryPassword attribute of the computer object. While it is possible to manually remove these old passwords via AD Users and Computers, integrating this task into a script streamlines the entire process.
After executing the script, only the new recovery key will remain in Active Directory Users and Computers.
To automate this, read the content of the relevant attribute using Get-ADObject. You can modify the script provided to query any hostname, although it initially queries the local computer object. It then deletes the existing recovery passwords before creating a new protector, ensuring each computer object contains only the currently valid recovery password.
Here is a Video on how to fix 0xc000007b Error on Windows 11, and Backup existing and new BitLocker Recovery Keys to Active Directory.
Script to Renew the Recovery Key
Ensure that you install the Active Directory module on the system before running the script. You can install the module via the RSAT (Remote Server Administration Tools) if it’s not already available.
This script checks if the Active Directory module is installed and installs it if it’s not found.
# Check if the Active Directory module is availableif (-not (Get-Module -ListAvailable -Name ActiveDirectory)) { Write-Host "Active Directory module not found. Installing..." # Install RSAT for Active Directory based on OS version $osVersion = [System.Environment]::OSVersion.Version if ($osVersion.Major -eq 10 -and $osVersion.Build -ge 17763) { # Windows 10 version 1809 or later Add-WindowsCapability -Online -Name "Rsat.ActiveDirectory.DS-LDS.Tools~~~~0.0.1.0" } elseif ($osVersion.Major -eq 10 -or $osVersion.Major -eq 6) { # Windows 10 earlier versions or Windows Server 2016 Install-WindowsFeature -Name "RSAT-AD-Tools" } else { Write-Error "Unsupported OS version. Please install RSAT manually." exit } # Import the module after installation Import-Module ActiveDirectory} else { Write-Host "Active Directory module is already installed."}# Proceed with the rest of your script# Your existing code here...

Script for performing BitLocker Rotation in AD
Here is a detailed script for renewing the BitLocker recovery key:
# Retrieve KeyProtectors of type RecoveryPassword$currentRecoveryPasswords = Get-BitLockerVolume -MountPoint $env:SystemDrive | Select-Object -ExpandProperty KeyProtector | Where-Object { $_.KeyProtectorType -eq 'RecoveryPassword' }# Add a new RecoveryPassword protector$newRecoveryPassword = Add-BitLockerKeyProtector -MountPoint $env:SystemDrive -RecoveryPasswordProtector -WarningAction SilentlyContinue# If a new protector is successfully created, delete the old oneif (($newRecoveryPassword.KeyProtector | Where-Object { $_.KeyProtectorType -eq 'RecoveryPassword' }).Count -gt $currentRecoveryPasswords.Count) { $currentRecoveryPasswords | ForEach-Object { Remove-BitLockerKeyProtector -MountPoint $env:SystemDrive -KeyProtectorId $_.KeyProtectorId | Out-Null }}# Get the computer object from Active Directory$computerObject = Get-ADComputer -Filter "Name -eq '$env:COMPUTERNAME'"# Retrieve stored RecoveryPasswords from Active Directory$storedRecoveryPasswords = Get-ADObject -SearchBase $computerObject -Filter { ObjectClass -eq 'msFVE-RecoveryInformation' } -Properties *# Delete old RecoveryPasswords from Active Directoryforeach ($storedRecoveryPassword in $storedRecoveryPasswords) { $currentRecoveryPasswords | ForEach-Object { if ($storedRecoveryPassword.'msFVE-RecoveryPassword' -eq $_.RecoveryPassword) { Write-Host "Removing old recovery password: $($storedRecoveryPassword.'msFVE-RecoveryPassword')" Remove-ADObject -Identity $storedRecoveryPassword -Confirm:$false } }}
After running the script, you can confirm that there are no old BitLocker passwords stored by using the following cmdlet.
manage-bde -protectors -get C:

See How to determine why an MBAM-protected device is non-compliant, and How to Import Data from a GitHub Repository to Postman.
Conclusion on BitLocker Recovery Key Rotation in AD
To maintain security, renewing the BitLocker recovery password is crucial, especially if you have exposed it while unlocking a drive.
FAQs on MBAM Key Recovery
Yes, the local deletion of a user profile can impact the authorisation of MBAM (Microsoft BitLocker Administration and Monitoring) self-service recovery. User profiles on a machine can store important information such as encryption keys, and user-specific settings.
If a user profile is deleted locally associated with that user might also be deleted, which could potentially disrupt access to BitLocker-encrypted drives and the ability to use MBAM self-service recovery.If the local profile is deleted and recreated, the new profile may not have the necessary associations with the MBAM service that the old profile had. This could mean that the self-service recovery tool does not recognize the user as authorized to perform the recovery
BitLocker lets users choose to encrypt just their data. Although it's not the most secure way to encrypt a drive, this option can reduce encryption time by more than 99 percent, depending on how much data that needs to be encrypted. For more information, see Used Disk Space Only encryption.
Policy settings can be configured to require that data drives be BitLocker-protected before a BitLocker-protected computer can write data to them. When these policy settings are enabled, the BitLocker-protected operating system will mount any data drives that aren't protected by BitLocker as read-only.
I hope you found this article on how to perform BitLocker recovery password rotation in Active Directory useful. Please feel free to leave a comment below.