Once a drive is encrypted by BitLocker, it can only be unlocked or decrypted with a Bitlocker password or the Bitlocker Recovery Key. And anyone without proper authentication will be denied access even if the computer has been stolen or the hard disk is taken. In this article, you will learn Why does MBAM not automatically re-encrypt MBAM or Bitlocker-protected devices. Please see how to uninstall your current version of MBAM and run setup again.
BitLocker uses Advanced Encryption Standard (AES) encryption algorithm with 128-bit or 256-bit keys for encrypting data in the entire drive or only used space of the drive.
We employ Group Policy Object to enforce BitLocker drive encryption on client computers in an enterprise environment. Here are some related guides: How to fix the MBAM Client Deployment is only supported on MBAM 2.5 SP1. See how to remove RDS Client Access Licenses from RDS Server.
When would you encounter this issue?
- By default, if you do not specify a different encryption method other than AES-128-bit. BitLocker will use the default encryption method (AES 128-bit). You will find more information in this Deploy management agent guide.
- If you disable or don’t configure these settings, BitLocker will use the default encryption method (AES 128-bit).
- You have already enabled BitLocker to protect my personal device and now there is an organization-wide policy to protect devices with MBAM to ensure compliance by all devices.
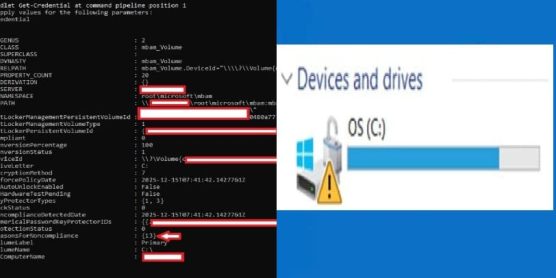
MBAM doesn’t re-encrypt drives that are already protected with BitLocker Drive Encryption. If you deploy a BitLocker management policy that doesn’t match the drive’s current protection, it reports as non-compliant. The drive is still protected.
For example, you have used BitLocker to encrypt the drive with AES-XTS 128 encryption algorithm, but the MBAM or the Configuration Manager policy requires AES-XTS 256. The drive is non-compliant with the policy, even though the drive is encrypted. Therefore, if a different encryption algorithm is not used, MBAM will not automatically re-encrypt the device.
Kindly refer to these related guides: How to unlock a fixed drive protected by BitLocker. How to deploy Microsoft BitLocker Administration and Monitoring Tool, and how to correctly disable Microsoft BitLocker Administration and Monitoring encrypted devices,
Resolution to MBAM not automatically re-encrypt Bitlocker-protected devices?
To work around this issue, you will need to first disable BitLocker on the device. Then deploy a new policy with the new settings that will apply the AES-XTS 256 encryption algorithm.
MBAM or the Configuration Manager is capable of taking over a BitLocker-protected device if it is automatically encrypted with the same encryption key (encryption algorithm).
Please see, Deploy a Static Website to Azure Storage from VSCode, how to Get your free Microsoft 365 E5 Sandbox today, and Microsoft Desktop Optimization Pack [MDOP] at a glance (AGPM, MBAM, App-V, DaRT, MED-V, and UE-V).
MBAM Drawback
The following are the things MBAM cannot do. You may want to see this guide for what MBAM cannot do such as “Effect of renaming an MBAM or BitLocker protected Computer“. The following are the things MBAM cannot do.
- Decrypt systems and re-encrypt with the right algorithms. We have already seen this multiple times.
- Automatically update a device that is renamed to a new name.
- Force users to change the PIN in XX number of days.
- Force a change to the recovery key in an xx number of days etc.”
FAQs on MBAM/BitLocker Protection on Windows
TPM stores Bitlocker keys and other secrets and key material while Secure Boot verifies signatures on boot software (UEFI firmware, EFI applications and the OS itself)
to ensure that they haven’t been subverted by a root kit.
– Boot Direct Memory Access (DMA) protection is part of Kernel DMA Protection which protects Bitlocker keys and other secrets stored in memory while the OS is running. Starting with Windows 10 version 1803, Intel-based devices have kernel protection against Boot DMA attacks via Thunderbolt3 ports enabled by default.
– During the boot process. We rely on security features implemented as part of the device hardware and firmware, TPM and Secure Boot. Newer devices have TPM and Secure Boot to mitigate any form of startup attack.
– Pre-boot Authentication
– Authentication after the user is unlocked
– BitLocker activation without a PIN (Password).
The Pre-boot Authentication” and “Authentication after the user is unlocked” can result in inconveniences. Users can forget their PIN or lose their startup key and will be denied access to their data. Until they are able to contact the support team to obtain a recovery key.
BitLocker PBA is good against memory attacks. This is because it stores the encryption keys in memory only after pre-boot authentication is completed. PBA is designed to prevent the encryption keys from being loaded to system memory. Without the trusted user supplying another authentication factor such as a PIN or a startup key.
I hope you found this blog post on “Why does MBAM not automatically re-encrypt MBAM or Bitlocker-protected devices?” helpful. If you have any questions, please let me know in the comment session.