Skip to content

TechDirectArchive

Hands-on IT, Cloud, Security, Veeam & DevOps

  • Home
  • About
  • Advertise With US
  • Reviews
  • Contact
  • Toggle search form

AWS Flow Logs IAM Role Setup

Posted on 09/03/201817/08/2026 Christian By Christian No Comments on AWS Flow Logs IAM Role Setup
  1. Home
  2. AWS/Azure/OpenShift
  3. AWS Flow Logs IAM Role Setup
Infographic showing steps to set up AWS CloudWatch Logs, including components like AWS Lambda Function, Amazon DynamoDB Table, Amazon CloudWatch Logs, AWS IAM Role, and relevant policies.

In this article, we shall discuss “AWS Flow Logs IAM Role Setup” To effectively monitor traffic within your VPC, subnet, or network interface using flow logs, it’s crucial to have the required permissions to create AWS Flow Logs roles. Please, see Logon Failure Reasons for Windows Event Viewer, how to Add and Remove Multiple Virtual Desktops in Windows, and KDC reply did not match expectations while getting initial credential.

However, this role enables the creation of flow logs for VPCs, subnets, or network traffic, ensuring comprehensive monitoring across all network interfaces within the designated VPC or subnet.

To enhance your AWS environment, create an AWS Flow Logs Role. However, This role ensures the efficient publishing of flow log data to a dedicated log group in CloudWatch Logs, with each network interface having its unique log stream.

Also, see How to add servers to the Trusted Hosts list, and Preparation failed: Error during connect in the default daemon configuration on Windows, the docker client must be run with elevated privileges.

Create an IAM role

To create an IAM role for flow logs, open the IAM console at https://console.aws.amazon.com/iam/.

In the navigation pane, choose Roles, Create role. Under Select type of trusted entity, choose AWS service (EC2, lambda and others) and select EC2 (Allow EC2 instance to call AWS services on your behalf)
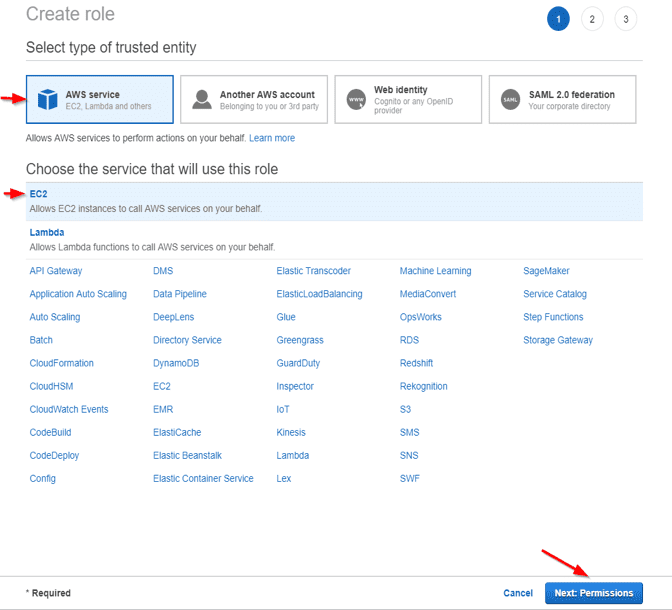
IAM Role

Choose Next: Permissions. On the attached permissions policies, Do not select anything and (click on Next: Review.
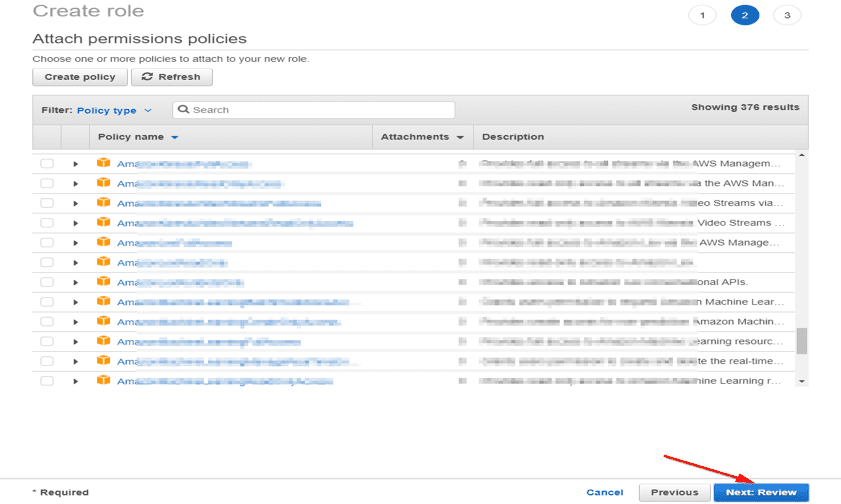
Network Monitoring

Enter a name for your role; for example, Chris-Flow-Logs-Role, and optionally provide a description. Choose Create role.
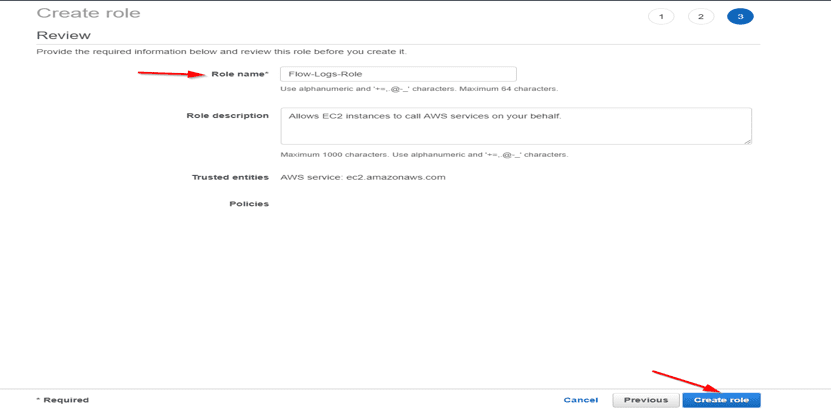
Cloud Security
AWS Flow Logs

Please, see Creating IAM Users, Adding MFA and Policies on AWS, How to prevent emails from going into a junk folder in Office365, and Administer Cisco ASA: Mastering CLI Management.

Add Policy

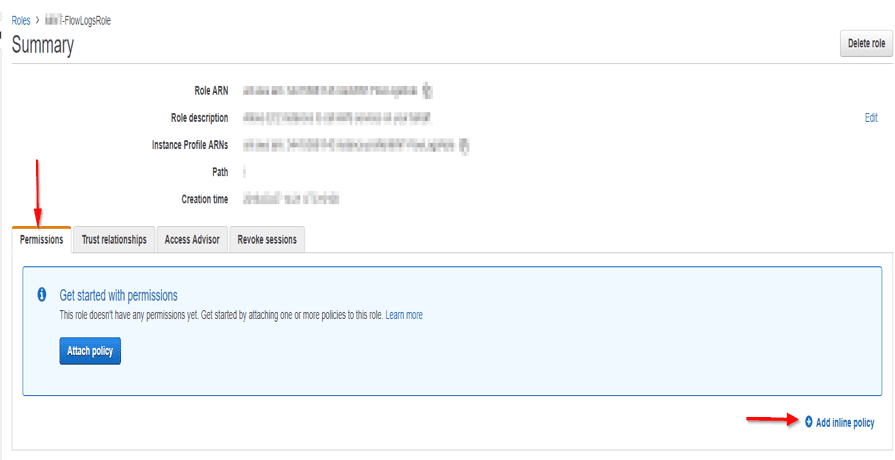
Moreover, After successfully creating the AWS Flow Logs Role, select its name and click to open it.

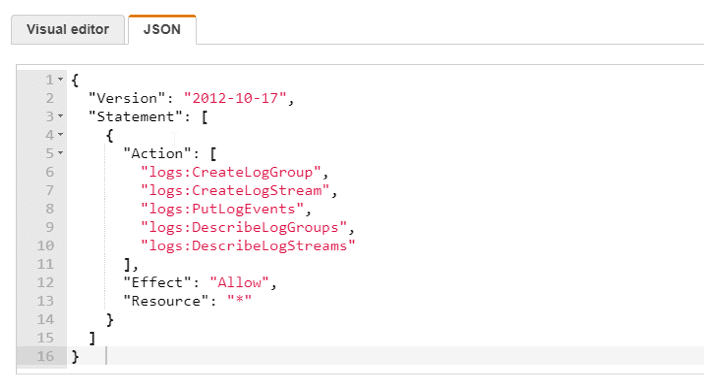
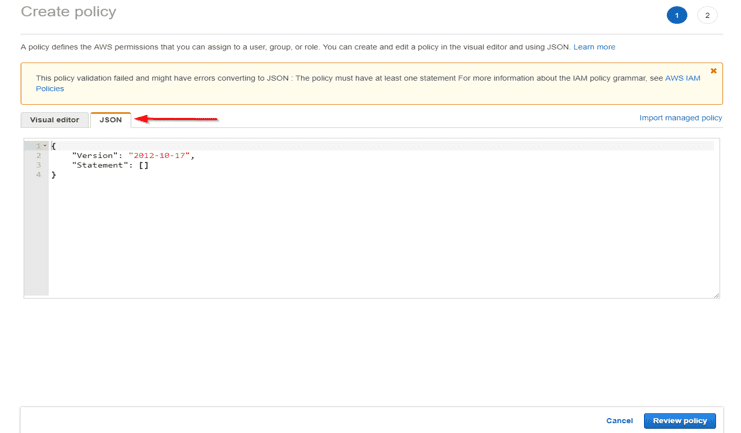
Under Permissions, choose to add inline policy. Choose the JSON tab as shown below
IAM Role

Nonetheless Navigate to this URL and copy the IAM Roles for Flow logs. Copy the IAM roles for flow logs and paste in the window as shown below

{
"Version": "2012-10-17",
"Statement": [
{
"Action": [
"logs:CreateLogGroup",
"logs:CreateLogStream",
"logs:PutLogEvents",
"logs:DescribeLogGroups",
"logs:DescribeLogStreams"
],
"Effect": "Allow",
"Resource": "*"
}
]
}
JSON snippet showing AWS IAM policy with actions related to CloudWatch logs and permissions.
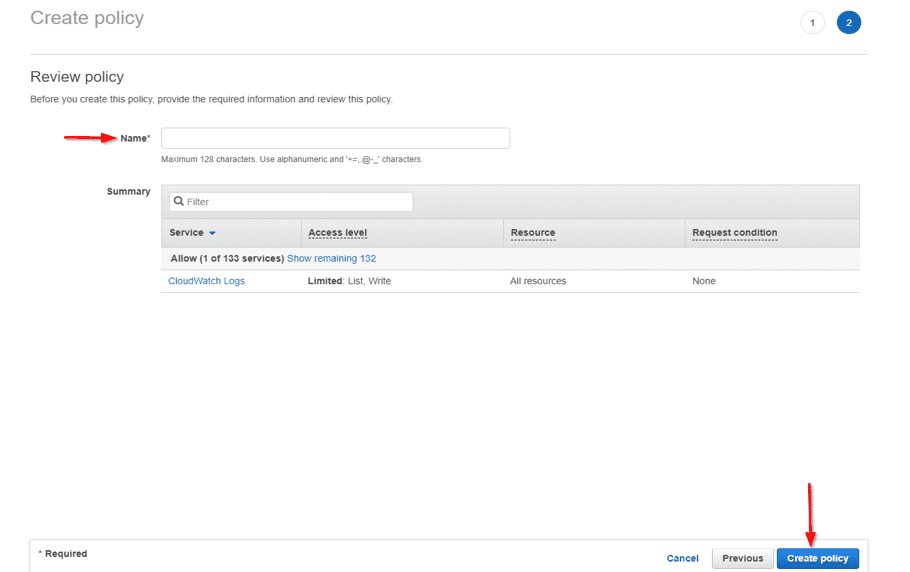
Screenshot of a policy creation interface, showing fields for 'Name,' 'Summary,' 'Access level,' and 'Payment Condition,' with a highlighted button for 'Create policy.'

– Choose Review policy.
– Enter a name for your policy, and then choose to Create policy.
– and then choose to Create policy.
– In the section, IAM Roles for Flow Logs created previously (i.e, click on the role)
–  In the section, IAM Roles for Flow Logs created previously,
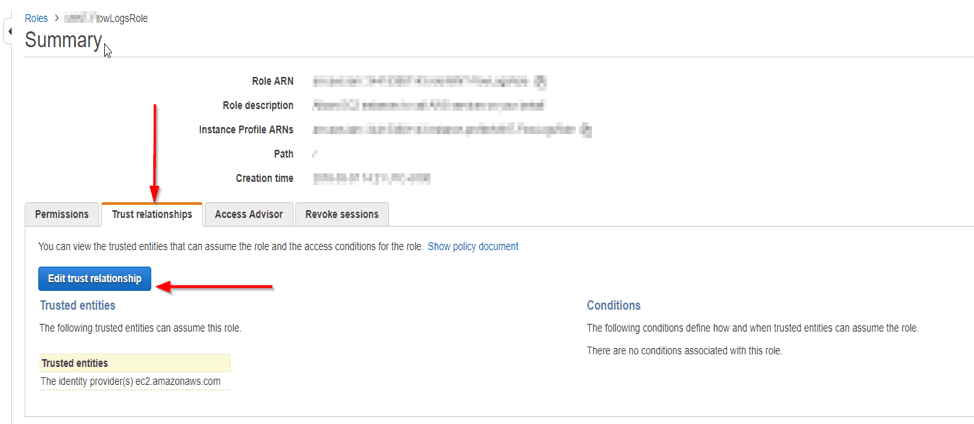
– choose Trust relationships
Screenshot of a summary page displaying permissions, trust relationships, and access controls with highlighted options.

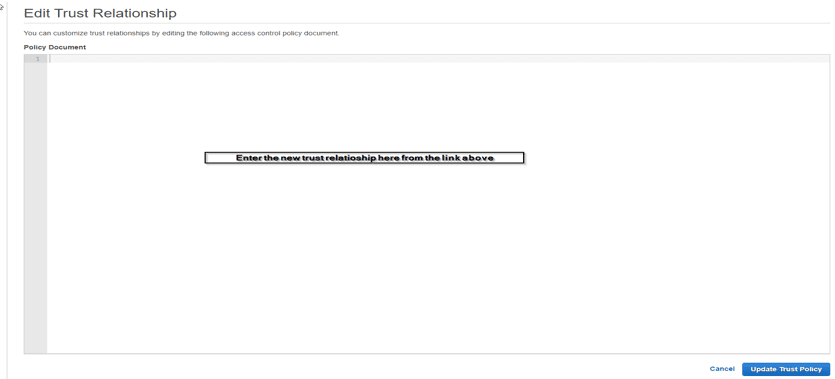
To optimize network monitoring. Start by editing the trust relationship, then proceed to delete the existing policy document.

Copy and paste in the new trust relationship policy from https://docs.aws.amazon.com/AmazonVPC/latest/UserGuide/flow-logs.html#flow-logs-iam
Screenshot of a user interface titled 'Edit Trust Relationship' with a text box prompting for policy document content.
{
"Version": "2012-10-17",
"Statement": [
{
"Sid": "",
"Effect": "Allow",
"Principal": {
"Service": "vpc-flow-logs.amazonaws.com"
},
"Action": "sts:AssumeRole"
}
]
}

Please, see Creating Profiles for your AWS Access Credentials for AWS Toolkit in Visual Studio, and MFA on Root Account: Create a User on AWS and Register MFA.

Update Trust Policy

When you are done, choose Update Trust Policy.

Note: On the Summary page, take note of the Role ARN for your role. You need this ARN when you create your flow log. To create a flow log, view flog and delete flow log, pls follow this URL below.

I hope you found this article on AWS Flow Logs IAM Role Setup very useful. Please, feel free to leave a comment below.

Thank you for reading this post. Kindly share it with others.

  • Share on X (Opens in new window) X
  • Share on Reddit (Opens in new window) Reddit
  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Facebook (Opens in new window) Facebook
  • Share on Pinterest (Opens in new window) Pinterest
  • Share on Tumblr (Opens in new window) Tumblr
  • Share on Telegram (Opens in new window) Telegram
  • Share on WhatsApp (Opens in new window) WhatsApp
  • Share on Mastodon (Opens in new window) Mastodon
  • Share on Bluesky (Opens in new window) Bluesky
AWS/Azure/OpenShift Tags:AWS, AWS Flow Logs IAM Role Setup, Flow logs

Post navigation

Previous Post: Upgrade ManageEngine Password Manager Pro
Next Post: Access EC2 Linux Instance via the Password

Related Posts

  • a Multiple SPF Records Issues and Examples@2x
    How to setup SPF and TXT Records in AWS AWS/Azure/OpenShift
  • CreateanAWSact
    How to Set up an Amazon Web Services (AWS) Account AWS/Azure/OpenShift
  • keyvault
    How To Use Azure Key Vault Secrets in Azure Pipelines AWS/Azure/OpenShift
  • Azure logo
    Microsoft Azure Active Directory: How to setup Azure AD Tenant AWS/Azure/OpenShift
  • ADV lab7 1 e1783202718190
    Azure Virtual Desktop: Build Custom Session Host Images Using Image Builder Templates [Part 07] AWS/Azure/OpenShift
  • banner2 1
    How to use GitHub as Source Provider for AWS CodePipeline AWS/Azure/OpenShift

More Related Articles

Install Packages to Amazon Virtual Machine Using Terraform How to Install Packages to Amazon VM using Terraform AWS/Azure/OpenShift
image 73 How to manage and use Amazon S3 access points using the AWS Management Console AWS/Azure/OpenShift
TLS1.2 Unable to install Azure AD Connect, TLS 1.2 is required: How to enable or disable TLS 1.2 on a Windows Server via the Registry and PowerShell AWS/Azure/OpenShift
S3 Bucket Access AWS Management Console and Create Resources with AWS CLI on Windows AWS/Azure/OpenShift
Azure Backup For AKS How to protect Azure Kubernetes Service (AKS) with Azure Backup AWS/Azure/OpenShift
How to configure Azure container register with secured connection with container apps Configure Azure Container Registry for a secure connection with Azure Container Apps AWS/Azure/OpenShift

Leave a Reply Cancel reply

You must be logged in to post a comment.

Microsoft MVP

vexpert-badge-stars-5

Virtual Background

VEEAMLEGEND

Categories

Top 30 Sysadmin blog

veeaam100

Veeam Vanguard

  • sdfgh 1
    How to fix “Unable to Sign In: Domain Not Available” Windows Server
  • main
    How to Move OneDrive Folder to a different location in Windows Windows
  • images
    Query MBAM to display the BitLocker Recovery report Network | Monitoring
  • Move Resources On Azure
    Move Azure Resources between Subscriptions AWS/Azure/OpenShift
  • Restrict the number of tabs a user can open in Chrome and Edge
    Restrict the number of tabs a user can open in Chrome and Edge Windows
  • Fix Windows Installer Service Could Not Be Accessed Error
    How to Fix the “Windows Installer Service Could Not Be Accessed” Error While Installing an Application Windows
  • change default apps windows 10 1
    Clean Install and PC Reset: How to perform a Fresh Start installation of Windows 10 Windows
  • image 6
    Set Browers and Windows to reopen Apps on Startup Windows

Subscribe to Blog via Email

Enter your email address to subscribe to this blog and receive notifications of new posts by email.

Join 1,746 other subscribers
  • RSS - Posts
  • RSS - Comments
  • About
  • Authors
  • Write for us
  • Contact
  • Advertise with us
  • General Terms and Conditions
  • Privacy policy
  • Feedly
  • Telegram
  • Youtube
  • Facebook
  • Instagram
  • LinkedIn
  • Tumblr
  • Pinterest
  • Twitter
  • mastodon
  • Bsky

Tags

Active Directory Azure Bitlocker Microsoft Windows PowerShell WDS Windows 10 Windows 11 Windows Deployment Services Windows Server 2016

Copyright © 2026 TechDirectArchive

Loading Comments...

You must be logged in to post a comment.