Skip to content

TechDirectArchive

Hands-on IT, Cloud, Security, Veeam & DevOps

  • Home
  • About
  • Advertise With US
  • Reviews
  • Contact
  • Toggle search form

Azure Resource Locks: Protecting Critical Cloud Resources from Accidental and Malicious Deletion

Posted on 12/05/202623/06/2026 Link State By Link State No Comments on Azure Resource Locks: Protecting Critical Cloud Resources from Accidental and Malicious Deletion
  1. Home
  2. AWS/Azure/OpenShift
  3. Azure Resource Locks: Protecting Critical Cloud Resources from Accidental and Malicious Deletion
Azure Resource Locks Protection

In modern cloud environments, infrastructure protection is no longer optional. Organizations operating on Microsoft Azure must ensure that business-critical workloads, networking components, storage accounts, and security services are protected not only from accidental human errors, but also from unauthorized or malicious actions. In this guide, we shall discuss “Azure Resource Locks: Protect Resources from Accidental deletion”. Please see How to Add a Delete Lock on Azure Resources, and Fix MDT accidental OS deletion.

One of the most effective governance mechanisms available in Azure is the Azure Resource Lock feature. Azure Resource Locks provide a native protection layer that prevents users from deleting or modifying resources, even when they have elevated permissions.

Azure Resource Manager (ARM) governance capabilities include these locks, and organizations commonly adopt them in enterprise landing zones, production subscriptions, and regulated environments.

Also, see How to disable automatic screen lock in Ubuntu Linux, how to Delete or Rename and Create a Protected Organisation Unit in AD, and Read-only Files: Saving Files in VIM Editor on Linux/Unix-like OS.

Why Azure Resource Locks Matter

Cloud administrators frequently face operational risks caused by:

  • Accidental deletion of production resources
  • Misconfigured automation pipelines
  • Unauthorized infrastructure modifications
  • Insider threats
  • Incomplete governance enforcement
  • Human error during maintenance activities

A single accidental deletion of a virtual network, Key Vault, storage account, or production database can result in downtime, data loss, and compliance violations.

Azure Resource Locks mitigate these risks by enforcing protection at the Azure Resource Manager control plane level. Once you apply a lock, Azure blocks the operation regardless of the permissions assigned through Azure RBAC.

This makes Resource Locks a critical component in enterprise-grade Azure governance strategies.

Please see Update WinPE Boot Images with Windows UEFI CA Certificates [Part 2], how to perform Tape Drive Cleaning in Practice, and Active Directory Vulnerability Assessment with Purple Knight: Domain Controller Owner Is Not an Administrator.

Types of Azure Resource Locks

Azure provides two lock levels:

1: CanNotDelete Lock

The CanNotDelete lock prevents a resource from being deleted while still allowing authorized users to modify it. Typical use cases include:

  • Production virtual machines
  • Critical storage accounts
  • Shared networking infrastructure
  • Backup vaults
  • Domain controllers
  • Key Vault instances

This lock is ideal when operational changes are still required but deletion must be strictly prevented.

2. ReadOnly Lock

The ReadOnly lock prevents both deletion and modification of a resource. When this lock is applied:

  • Resources can still be viewed
  • Configuration changes are blocked
  • Update operations fail
  • Delete operations fail

A ReadOnly lock effectively limits interactions to read operations only, similar to assigning Reader-level behavior across all users. This model is particularly useful for:

  • Security baselines
  • Compliance-sensitive environments
  • Immutable infrastructure patterns
  • Golden configuration templates

Please see Fix Operating System Loader failed signature verification” on Dell Safe BIOS Systems via PXE [Part 3], and how to protect Microsoft 365 beyond native limits with VDC [Part 1].

Lock Inheritance Model

One of the most important concepts in Azure Resource Locks is inheritance. Locks applied at a higher scope automatically propagate to child resources. Azure supports locks at three levels:

  • Subscription
  • Resource Group
  • Individual Resource

For example:

  • A lock applied to a Resource Group automatically protects all resources inside that group
  • A lock applied at Subscription level affects every contained Resource Group and resource

This hierarchical inheritance guarantees consistent governance across large-scale Azure environments.

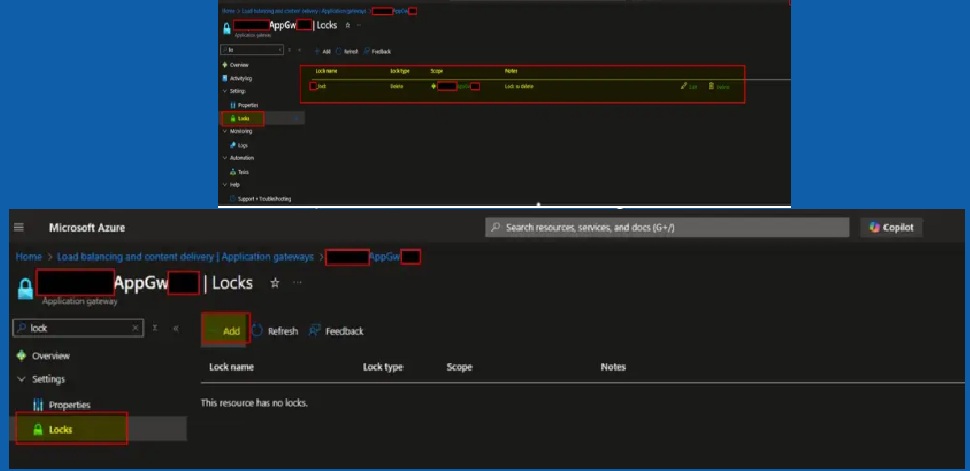
Choose the resource you want to protect. In this example, I will apply a lock on delete to the ‘Application Gateway’ resource:

Azure Lock 01

In the left-hand panel, look for ‘Lock’ and select “Add”:

Azure Lock 02

Fill in the forms and select the setting that suits your needs: ‘Lock on delete’ or ‘Read Only’:

Azure Lock 03

You have created your resource lock:

Azure Lock 04

I hope you found this article on “Azure Resource Locks: Protect Resources from Accidental deletion” very useful. Please feel free to leave a comment below.

Thank you for reading this post. Kindly share it with others.

  • Share on X (Opens in new window) X
  • Share on Reddit (Opens in new window) Reddit
  • Share on LinkedIn (Opens in new window) LinkedIn
  • Share on Facebook (Opens in new window) Facebook
  • Share on Pinterest (Opens in new window) Pinterest
  • Share on Tumblr (Opens in new window) Tumblr
  • Share on Telegram (Opens in new window) Telegram
  • Share on WhatsApp (Opens in new window) WhatsApp
  • Share on Mastodon (Opens in new window) Mastodon
  • Share on Bluesky (Opens in new window) Bluesky
AWS/Azure/OpenShift Tags:Azure delete lock configuration, Azure infrastructure protection, Azure management locks best practices, Azure ReadOnly lock setup, Azure resource deletion protection, Azure Resource Locks, Azure Resource Locks: Protecting Critical Cloud Resources from Accidental and Malicious Deletion, Azure subscription resource locks, malicious deletion prevention Azure, prevent accidental deletion Azure, protect Azure resources from deletion, secure Azure cloud resources

Post navigation

Previous Post: Fix Operating System Loader failed signature verification” on Dell Safe BIOS Systems via PXE [Part 3]
Next Post: Advanced Tape Troubleshooting: Diagnosing Veeam LTO Drive Issues with ITDT

Related Posts

  • a Multiple SPF Records Issues and Examples@2x
    How to setup SPF and TXT Records in AWS AWS/Azure/OpenShift
  • Screenshot 2024 02 29 at 8.03.48 PM
    How to create an Elastic Beanstalk environment in AWS AWS/Azure/OpenShift
  • elastic ip association error screen
    Fix Elastic IP Address Could not be Associated AWS/Azure/OpenShift
  • EC2 Public IP
    How to Allocate, Associate, Disassociate and Release Elastic IP Address from an EC2 Instance AWS/Azure/OpenShift
  • Create AWS RDS instance
    How to create an Amazon Relational Database Service Instance AWS/Azure/OpenShift
  • HybridCloudTrust
    WHFB Hybrid Cloud Kerberos Trust Model is now available AWS/Azure/OpenShift

More Related Articles

APIFEATURE Benefits of Azure API Management and how to create an API instance AWS/Azure/OpenShift
Set a Resource Delete Lock How to Add a Delete Lock on Azure Resources AWS/Azure/OpenShift
Azure Backup For AKS How to protect Azure Kubernetes Service (AKS) with Azure Backup AWS/Azure/OpenShift
Amazon Import Virtual Machines to AWS as AMI AWS/Azure/OpenShift
Angular Azure How to deploy your Angular App to Azure from Visual Studio Code AWS/Azure/OpenShift
Screenshot 2022 03 20 at 21.08.50 How to integrate AWS CodeBuild and AWS CodeCommit to SonarCloud AWS/Azure/OpenShift

Leave a Reply Cancel reply

You must be logged in to post a comment.

Microsoft MVP

vexpert-badge-stars-5

Virtual Background

VEEAMLEGEND

Categories

Top 30 Sysadmin blog

veeaam100

Veeam Vanguard

  • images 5
    How to use the Pleasant Password Server tool Password Manager
  • Git not Recognized Image banner
    Fix Git is not recognised as an internal or external command Version Control System
  • unnamed
    Remove Xbox from automatic startup: How to enable and disable automatic startup in Windows 11 Windows
  • banner 1
    Deploying Next.Js App Using Heroku Cloud Application Platform Version Control System
  • nodejs install on ubuntu
    How to install Node.js on Ubuntu Linux
  • Windows 11 Taskmanager
    Create Task Manager Shortcuts: How to add access, pin the Task Manager on Windows 11 Windows
  • Azure File Sync
    Azure File Sync : How to enable Self-Service restore AWS/Azure/OpenShift
  • ffd
    Unable to bind to LDAP or AD in Pleasant Password Server Password Manager

Subscribe to Blog via Email

Enter your email address to subscribe to this blog and receive notifications of new posts by email.

Join 1,747 other subscribers
  • RSS - Posts
  • RSS - Comments
  • About
  • Authors
  • Write for us
  • Contact
  • Advertise with us
  • General Terms and Conditions
  • Privacy policy
  • Feedly
  • Telegram
  • Youtube
  • Facebook
  • Instagram
  • LinkedIn
  • Tumblr
  • Pinterest
  • Twitter
  • mastodon
  • Bsky

Tags

Active Directory Azure Bitlocker Microsoft Windows PowerShell WDS Windows 10 Windows 11 Windows Deployment Services Windows Server 2016

Copyright © 2026 TechDirectArchive

Loading Comments...

You must be logged in to post a comment.